
Product Security
Sony positions the security of products and network services provided to customers as one of the important quality requirements. We strive to maintain security quality with due consideration for the safety and security of customers and all stakeholers, and to prevent the occurrence of issues that could threaten them. We will continue to promote initiatives to further enhance security quality so that customers around the world can use Sony products and network services safely and continuously with confidence.
Product Security Framework
Sony has configured its quality management system by defining quality management mechanisms across all processes, from product planning, development, design and manufacturing to sales and customer service. This has included defining the roles, responsibilities and authority of those responsible for product and customer service quality and establishing guidelines.
For product security as well, Sony works to ensure and continuously improve security quality based on this quality management system framework.
For details on the quality management framework, please refer to the link below.
Sony has a function for collecting security risk-related information from outside experts, researchers and other individuals. Sony assigns managers responsible for the software security of products and has a dedicated department for this purpose. The department coordinates with business units to address issues with the security of products. Based on the information received, the department assesses the impact of risk on customers from a software security perspective and implements appropriate measures.
Secure Development Process
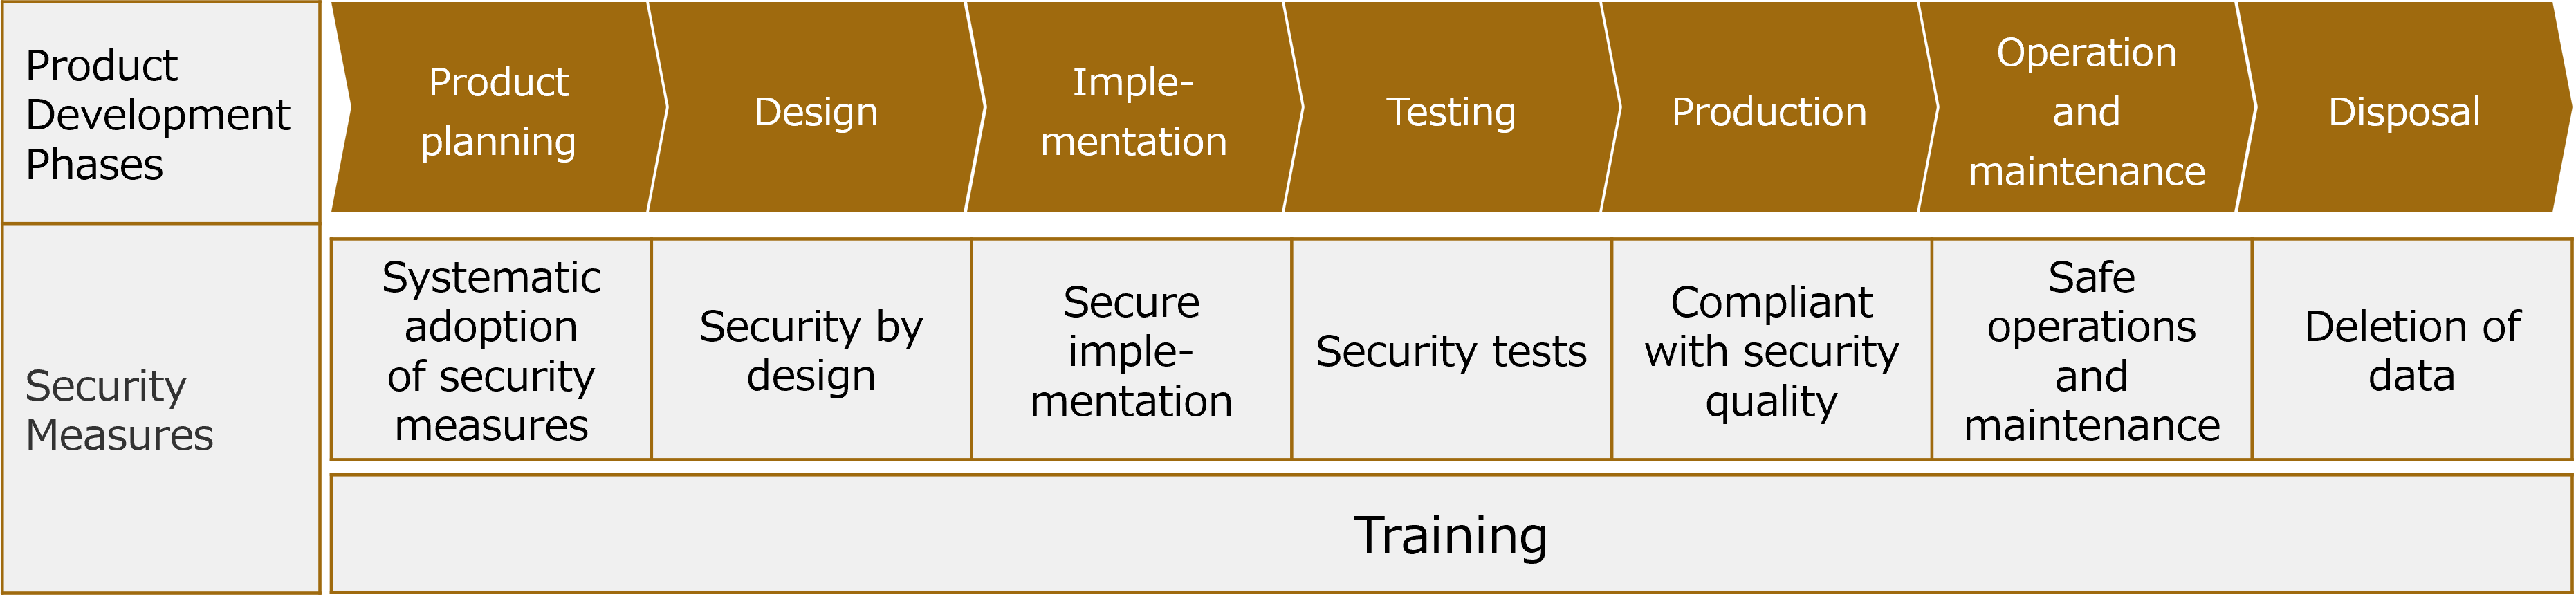
Sony implements security design and response systems in order to deliver products that customers can use with confidence. In 2012, the Sony Security Development Lifecycle was formulated as measures and rules to enhance security quality throughout each phase, from product development and network service planning right up to the time the product is discarded or the network service is terminated. As part of this process, it subjects products and network services to pre-shipping and pre-release inspections, including security risk assessments and the use of product security vulnerability detection tools.
These measures and rules are in place for all Sony products and network services, and regular inspections and audits are performed to ensure that they are being adhered to. Sony has also established internal guidelines pertaining to the security of products. It regularly reviews and updates these guidelines, and continues to implement employee training programs to enhance product security.
Sony Security Development Lifecycle
Development processes in product development focused on improving the security quality of products and network services
Due to growing societal concern and increasing demands regarding security issues, regulators in various countries/regions are developing new laws and regulations concerning product security. Sony has included requirements for conformance to product security regulations in the Sony Security Development Lifecycle. It is also establishing internal frameworks for collating and ensuring compliance with regulatory requirements in individual countries and regions.
Vulnerability Disclosure Policy
Sony accepts reports of security vulnerabilities related to our products and associated services in accordance with our Vulnerability Disclosure Policy and addresses them responsibly. For more details about the policy, please refer to the Sony-managed HackerOne programs listed below:
How to Report a Security Vulnerability
Sony is committed to responding to security vulnerabilities in an appropriate manner. We operate Secure@Sony program to receive security vulnerability reports from customers and security researchers regarding Sony products and associated services. If you believe you have identified a security vulnerability, please report it through the link below.
Sony Group Vulnerability Reporting Program (Secure@Sony)